Bring your users, groups and devices. Start with the identity systems you already use.
Your rules. Every agent.
Authorization
infrastructure
for AI agents.
Let agents work.
Keep control of what they can do.
Keydris checks each connected request. Allow it, ask for approval, or stop it.
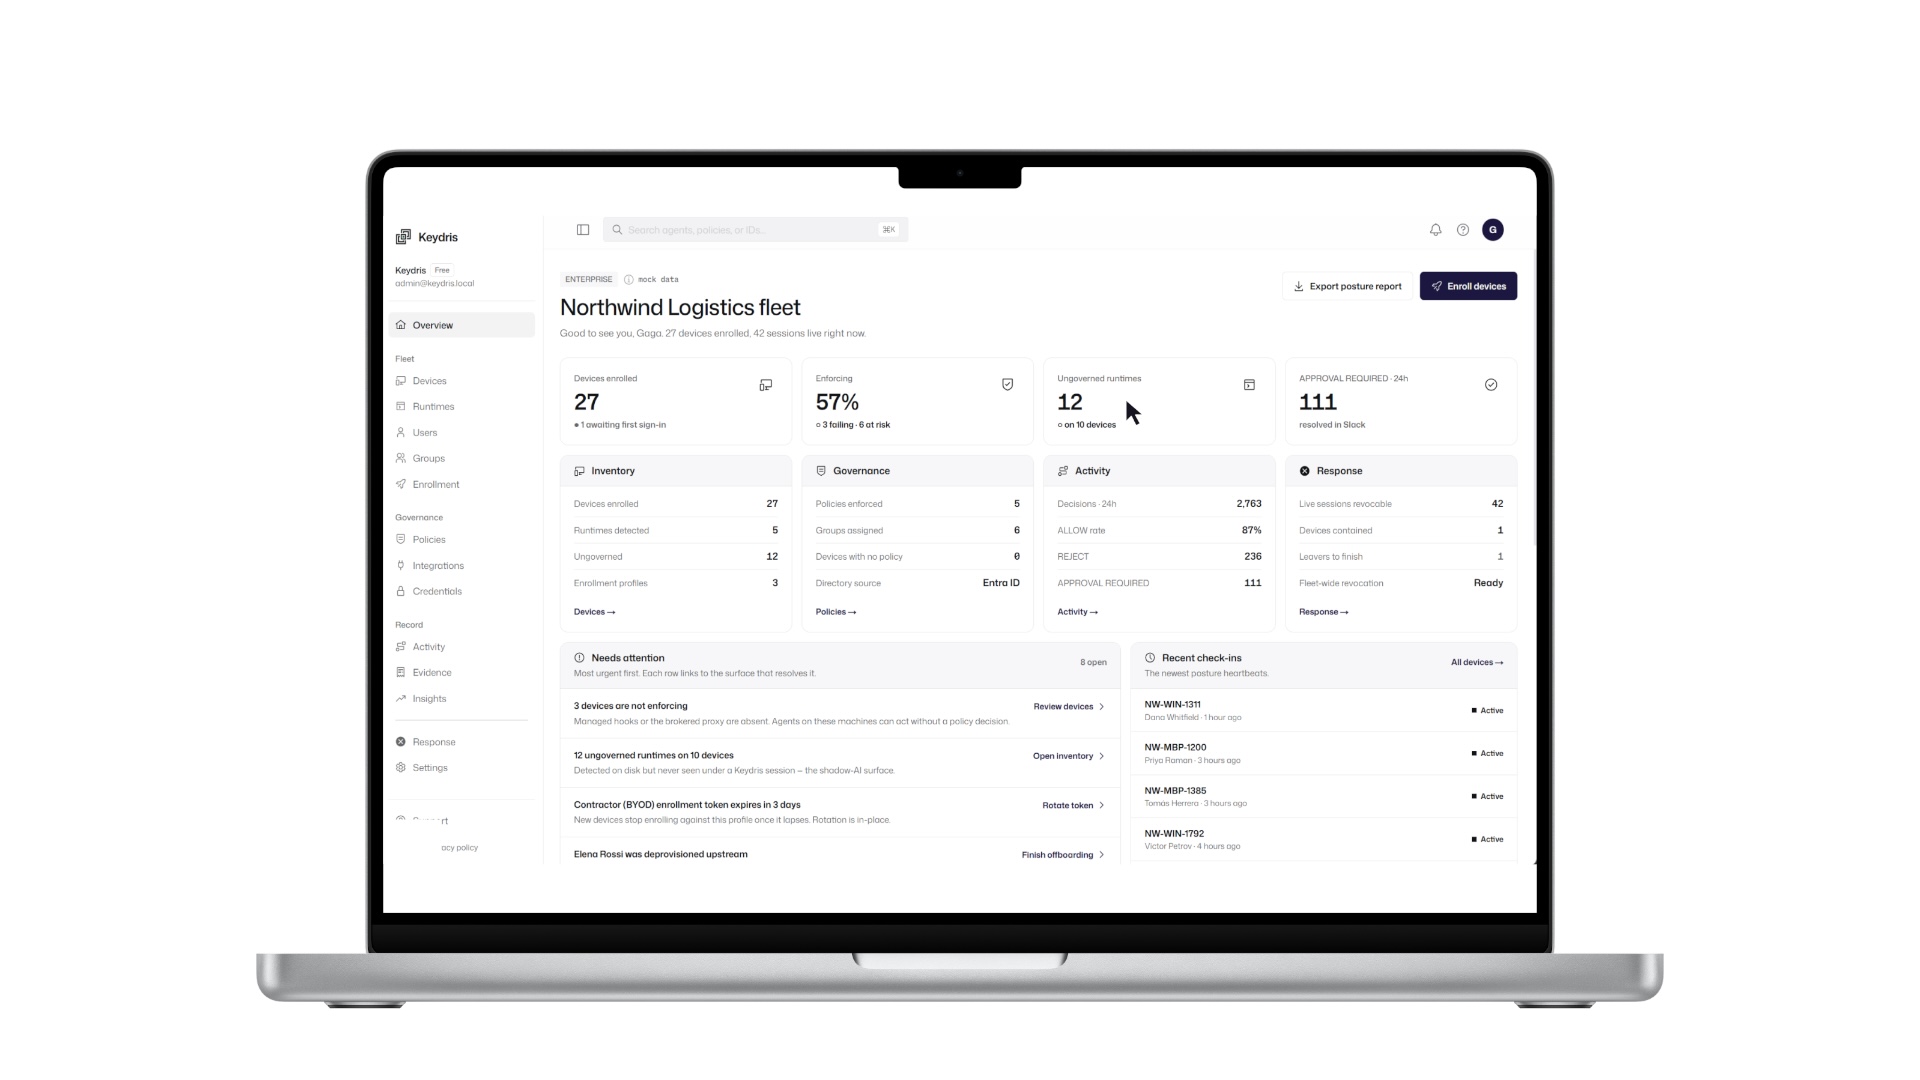
A stationary MacBook introduces Keydris. The app expands into screen close-ups for runtimes, request evidence, policy building and fleet review. The policy view follows the cursor through its controls without showing the bezel, then returns to the stationary MacBook at the end.
Connected to your enterpriseYour stack. Your rules.
Explore security Your stack. Your rules.
Every action accounted for.
Start with the identity systems your people already use. Connect their tools, define their authority, and carry your policies all the way to the action.
Connect the tools your people work with. Carry their identity into each governed action.
Define what can continue, what needs a reviewer and what must stop.
Give every governed action a clear outcome. Keep a record of the decision.
01 / Identity
Your enterprise is the starting point.
People, groups and devices give every request its context. Policy follows the signed-in user.
Enterprise context
UsersGroupsDevices
Identity attached to the requestThe AI agent blind spot
AI agents are spreading.
So are the risks.
Unseen agents
82%
of enterprises have discovered unknown or shadow AI agents operating in their environments.
Cloud Security Alliance · 2026Exceeded permissions
53%
of organizations have experienced AI agents exceeding their intended permissions.
Cloud Security Alliance · 2026Unapproved AI tools
80%
of employees use AI tools not approved by their organizations.
Cloud Security Alliance · 2026One authority layer.
From person to action.
Your people. Your rules. A check before each connected action.
People & teams
Use your existing teams.
Planned: connect your directory and use the people and teams you already manage.
Talk through your setupPeople & teamsPlanned connection
Lena Morgan
Finance · Signed-in user
TeamFinance
Allowed workInternal reporting
The person’s rules apply.
Team rules
Set clear rules.
Choose what each team’s agents can do, and when someone must approve.
Talk through your setupFinance team policy
Read internal reportsAllow
Export client recordsApproval required
Access another team’s filesReject
Planned device service
Apply rules on devices.
Planned: a device service checks connected actions and applies the signed-in person’s rules.
Talk through your setupManaged workspace
Lena Morgan
Finance policy
Read internal reportsAllow
Inside Keydris
A clear view.
Control where it counts.
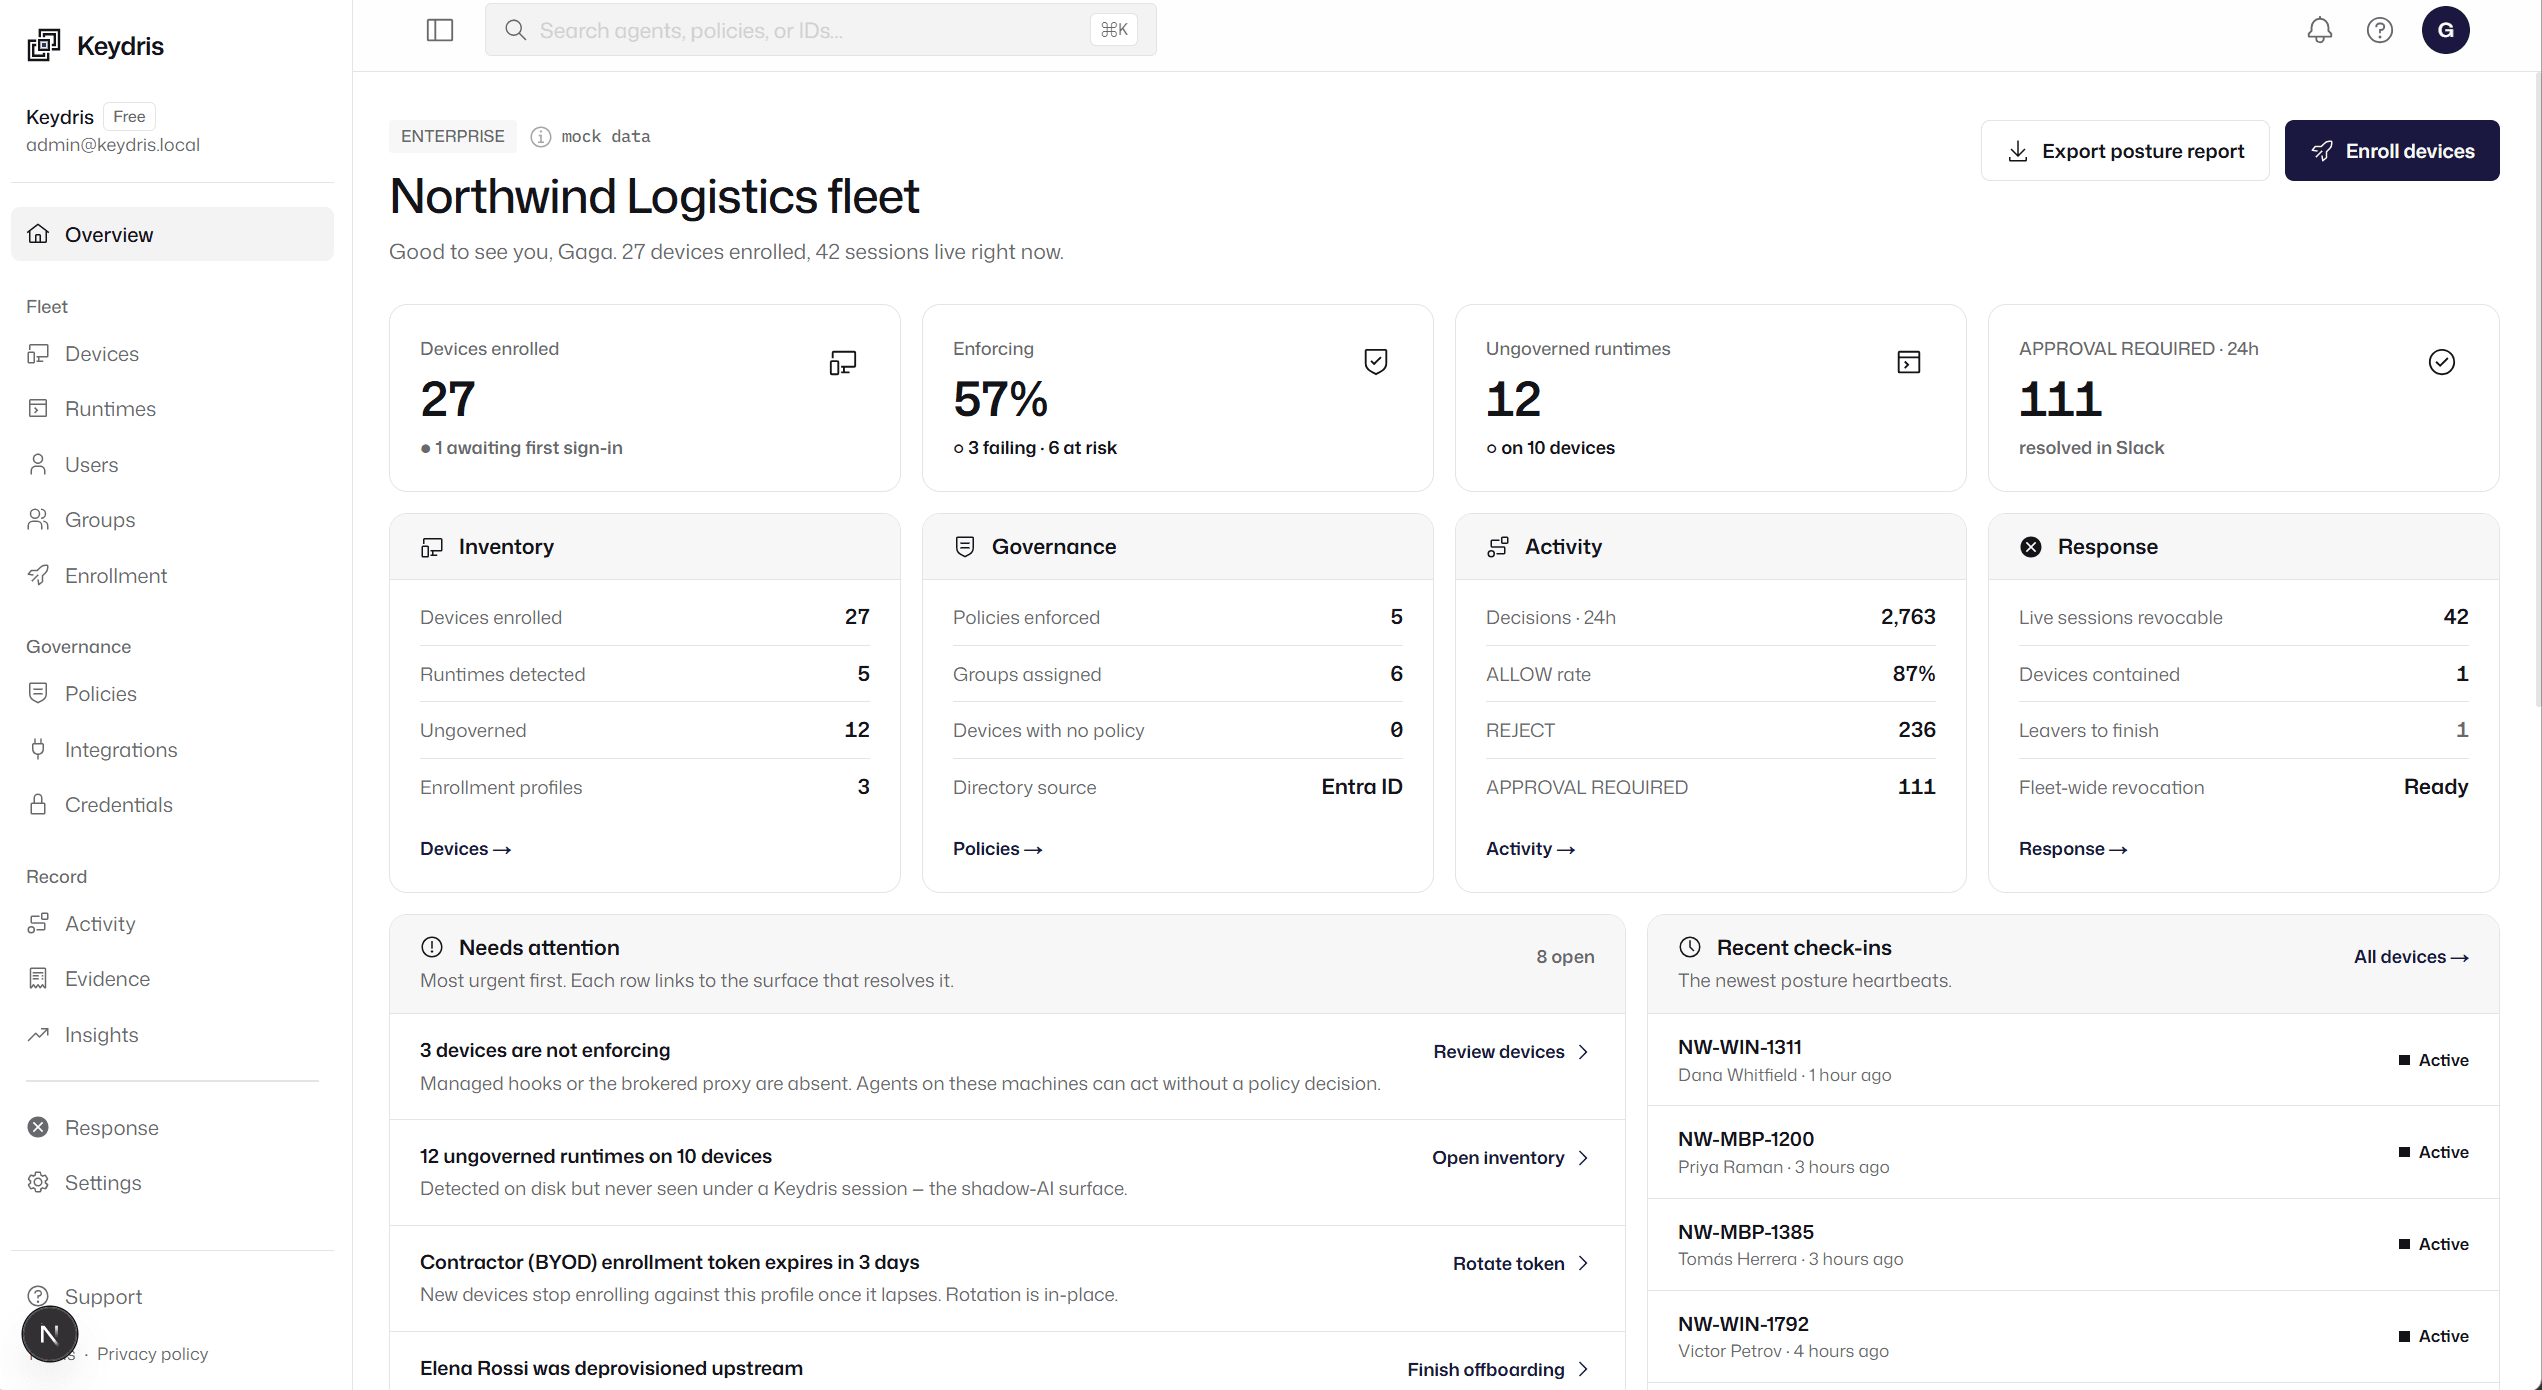
Your people, agents and decisions.
Together in one workspace.
See your devices, agents and the work that needs attention.
Find the agents in use and see where your rules apply.
Bring your teams together. See which rules belong to each one.
See what was allowed, what was blocked and what needed approval.
Review affected devices and stop access when you need to.
Our thinking
Software is beginning to act.
Why AI agents need clear limits before they act.
Or read it online firstFAQ
The questions a technical founder, platform engineer, or security reviewer should ask before adopting new infrastructure.
The basics
What is Keydris?
Keydris lets you control what AI agents can do before they do it. You define a policy that says what an agent is allowed to do. When the agent attempts a governed action, that action is checked against the policy before it runs, and the result is enforced: ALLOW, APPROVAL REQUIRED, or REJECT. You can let an agent read a repository, require human approval before it merges a pull request, or revoke its authority so the next action it attempts fails verification. Revoking does not stop the agent process or undo work it already finished. Keydris makes the authorization decision. The action itself runs in the system that owns it.
Is Keydris identity, authentication, or an MCP gateway?
No. Keydris is the authorization layer for AI agents. It is not an identity provider, agent runtime, monitoring product, or universal traffic proxy.
Why shouldn’t I build scoped checks myself?
You can build pieces of the model yourself. Keydris is for teams that want the policy, authority issuance, per-action verification, revocation, administration, and decision evidence to operate as one governed system across supported integrations. The public docs and CLI let you evaluate that tradeoff directly.
Your existing stack
Why isn’t OAuth or IAM enough?
OAuth, IAM, service accounts, and workload identity establish who or what has access. Keydris works alongside them and adds a per-action authority check: whether this specific governed action is inside the policy assigned to this agent right now.
Architecture and data
Where does verification happen? Can it complete locally?
The receiving boundary evaluates the governed action by requesting verification from the Keydris platform. That boundary can run in your environment, but it does not evaluate the policy by itself.
Does Keydris proxy my traffic or see my payloads?
Keydris does not claim to be a universal proxy for your application traffic. On supported self-hosted paths, payload traffic stays inside your environment and authorization information crosses to Keydris. On third-party systems a Keydris integration may participate in the data path. Keydris does not claim it is never in any data path.
Does Keydris publish a latency benchmark?
Not yet. The current public material makes no latency claim. Evaluate the supported architecture and integration paths in the documentation rather than relying on an unsourced performance adjective.
Revocation and evidence
What exactly gets revoked? Can the agent keep running?
The authority is revoked, not the agent process. The agent may continue running and attempting actions, but revoked authority fails subsequent verification.
What does the decision record prove?
A decision record preserves the evaluated action, agent, scope, policy version, checks, outcome, and timestamp for review and export. It is evidence of what the system checked and decided, not a guarantee of universal safety or compliance, and not a copy of the underlying request payload.
In your demo
- 1Choose an action
Bring one task your team wants AI to do.
- 2Set the rules
Decide what’s allowed and who approves.
- 3Plan the setup
See how it could connect to your tools.